Bloomberg: Russia-linked hackers exploit poorly secured industrial systems to sabotage Western infrastructure
Since Russia's full-scale invasion of Ukraine, Moscow-linked hacker groups have been targeting water facilities, factories and food companies in the West, Bloomberg reports. The attacks have burst pipes, spoiled food and started fires.
Hacker groups linked to Russia have in recent years gone beyond attacking the websites of Western government and private organizations, and are now hitting critical infrastructure and businesses. That is the central finding of a lengthy Bloomberg investigation summarized by the outlet Meduza. Targets have included water facilities, factories and food producers, with consequences ranging from burst pipes to spoiled food and fires. The cases show how poorly protected industrial control systems can become a genuine security risk.
What was hit
In Spain, between late 2024 and summer 2026, crematorium ovens at a funeral home in Alicante province stopped working. At a factory in Catalonia that makes transformers for renewable energy systems, equipment malfunctioned and a fire broke out. Two wineries halted operations after their heating and ventilation systems were disrupted and temperatures rose sharply in production and storage areas.
In the Danish village of Tureby, 450 homes lost their water supply in mid-December 2024 because the pressure setting in the control system had been set to zero. The next day pressure surged and underground pipes burst. Jan Hansen, who chaired the local water supply committee, later admitted that a cheap system had been chosen, with the password 1234.
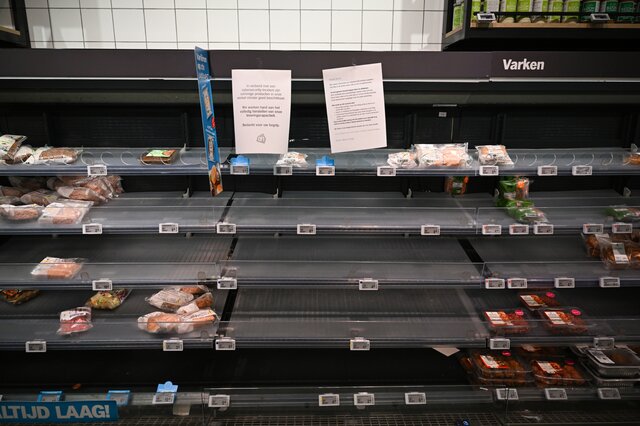
In the United States in 2024, hackers shut off refrigeration at a meatpacking plant near Los Angeles, spoiling more than 900 kilograms of meat; an ammonia leak forced workers to evacuate. In Texas, attackers changed control settings at a public water system, spilling an unknown amount of drinking water from storage tanks. In Pennsylvania, they tampered with equipment used to kill bacteria at a waste treatment facility.
Who is behind it
Bloomberg points to Cyber Army of Russia Reborn (CARR), a group linked to Russia's military intelligence agency, the GRU, whose members are under US and EU sanctions. In September 2024, members of CARR and NoName057(16) formed Z-Pentest, which focuses on industrial sabotage and is also sanctioned by the EU.
The US Justice Department accused Ukrainian citizen Victoria Dubranova in late 2025 of taking part in attacks on Russia's behalf; she is in custody and denies the charges. Italian citizen Chris Barlati was arrested in Spain in March, has pleaded not guilty and is not in custody.
Expert views
Experts say the hackers mostly exploit weaknesses in poorly secured systems. Cian Heasley of British firm Acumen Cyber said he is surprised a catastrophe has not yet happened. The US cybersecurity agency CISA says the groups are opportunistic and tend to exaggerate the impact of their attacks.