Overheating fridges and a fake alert: UK cyber agency warns of a wave of attacks
After attacks on commercial refrigeration across Europe, the record Binance crypto heist and a fake nuclear alert in Kyiv, the head of the UK's National Cyber Security Centre warns of a sharp rise in incidents. Experts agree AI is exposing vulnerabilities but differ on how exceptional the moment is.
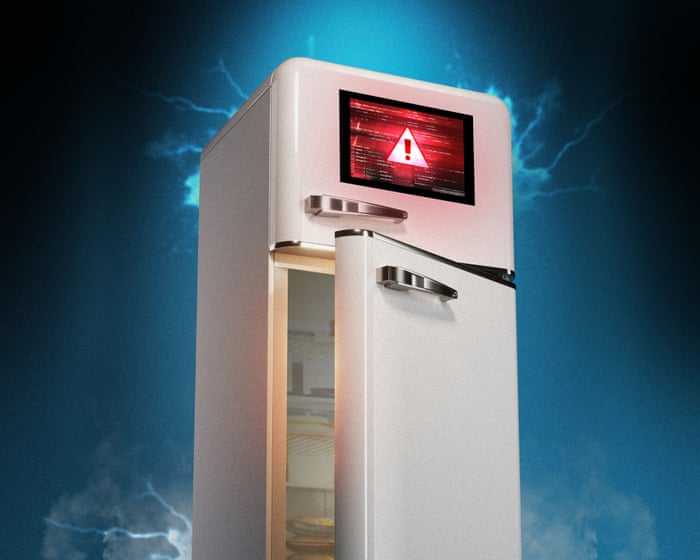
Hackers attacked internet-connected commercial refrigeration control systems in the UK and several other European countries last Monday. Alex Pearce, who runs a fruit and vegetable wholesale business in London, noticed that his units were showing 150C and unplugged the internet cable. Retailers in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands and Sweden reported similar problems the same day, with temperatures in some fridges and freezers climbing as high as 50C. Pearce said that had it happened on a Saturday morning, when nobody is at his premises, it could have led to a fire.
Three attacks within days
It was one of three incidents in a short period. On 30 October, hackers stole $6.3bn from Binance, the world's largest cryptocurrency exchange, in a record heist. On 1 November, an attack on Ukraine's emergency alert app sent residents of Kyiv a fake nuclear strike warning.
Richard Horne, head of the UK's National Cyber Security Centre (NCSC, part of the GCHQ intelligence agency), said the world is in the "foothills" of a new hacking landscape. He said the most serious short-term risk is a huge rise in the number of incidents. The centre forecasts that AI-powered malicious software will "highly likely" be used against UK power stations, airports and hospitals by 2028.
Who is behind it
The Binance theft has been attributed to the North Korean state. One expert sees Russian hallmarks in the fridge attacks but says certainty is lacking. NCSC director of operations Paul Chichester noted the attackers did not need AI, because the flaws were already known, including default passwords published in a manufacturer's manuals. Danfoss, a Danish firm and one of the affected system providers, said most of the affected equipment was old and no longer received security updates.
Ciaran Martin, the NCSC's founding chief executive, rejected comparisons with a "Wuhan moment", saying this is one of the waves of incidents that occur every few years. Since April, when Anthropic released its Mythos model, the number of vulnerabilities found by leading tech companies has risen eight-fold, though attacks have not grown at the same rate.